Convoys · Compliance and Assurance · Compliance App
The Compliance App.
An add-on to the Compliance and Assurance Convoy, in which the people who answer for a regime read its evidence themselves: auditors, compliance leads and the owners of the applications in the cluster. It runs in your own cluster, beside the convoy, signs people in through your identity provider, and records every request in an access log. The reports never leave the cluster.
The Compliance App is available, at USD 12,000 per organisation, per year, whatever the number of regimes. The screenshots on this page are of the released app, signed in as each role, on a test cluster with sample workloads.
What it is
The report, read where it is written.
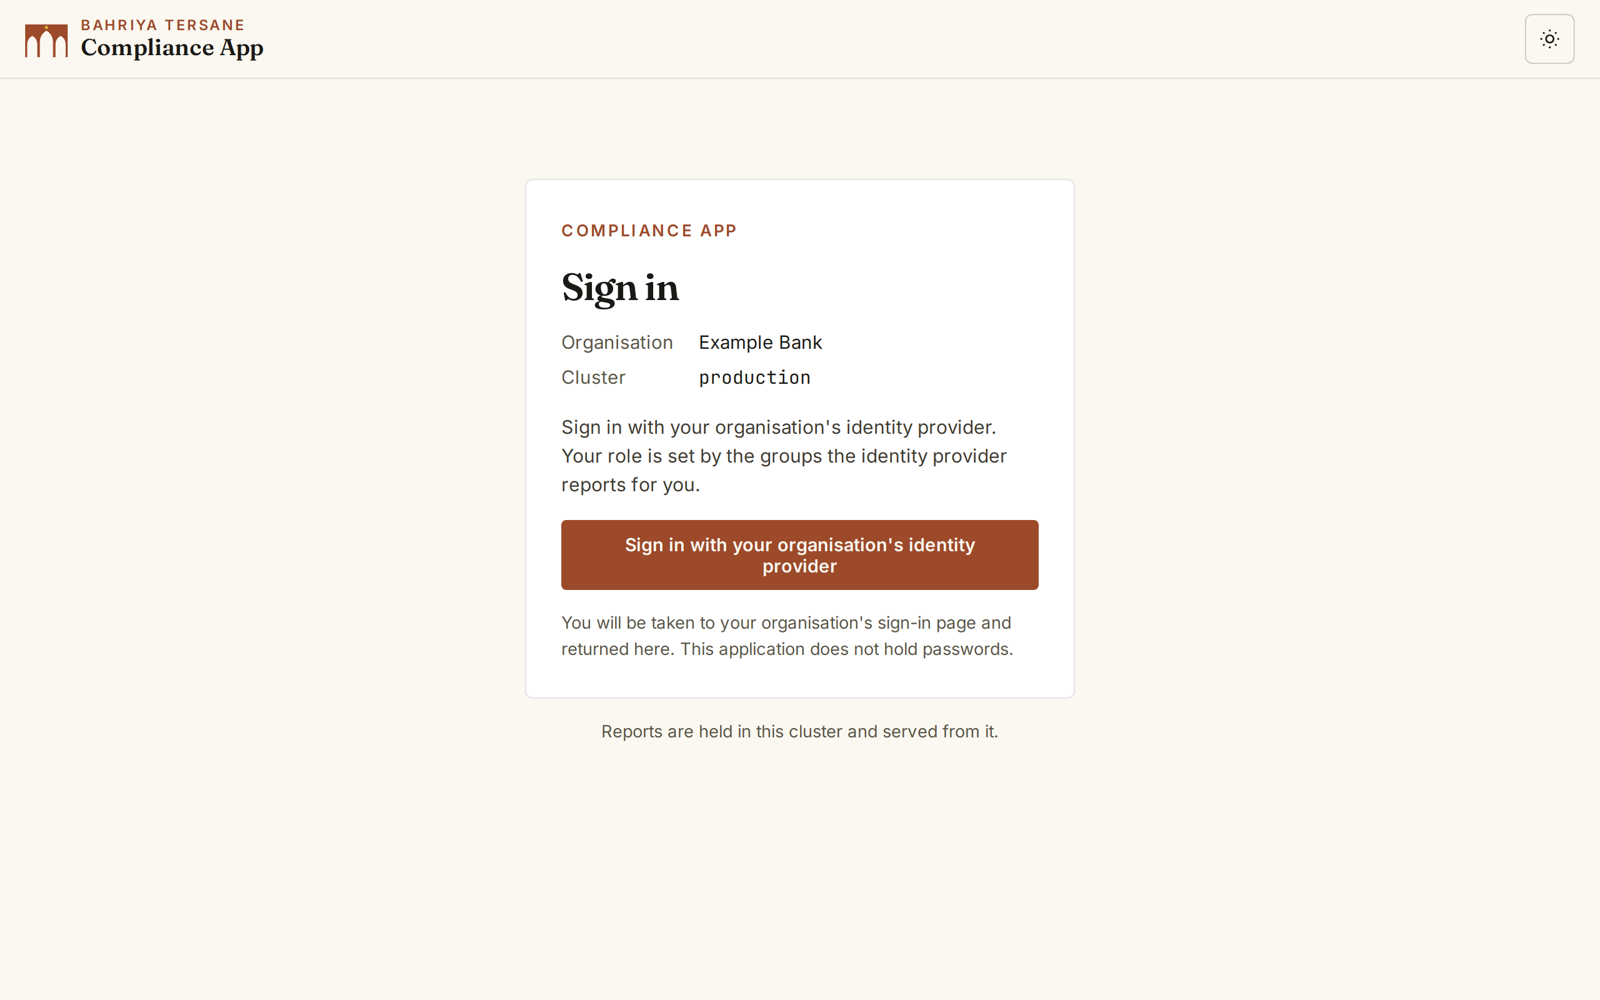
The convoy writes a dated report for each regime every day, in the regulator's own numbering. Without the app, reading it means asking whoever operates the cluster for a copy. With it, each person signs in and reads the evidence directly, at the level their role allows.
The app reads the convoy's evidence where the convoy writes it, read-only. It holds no Kubernetes service account token and needs nothing from the Kubernetes API. It sends nothing out of the cluster: the reports, the evidence and the record of who read them stay on your own volumes.
Sign-in
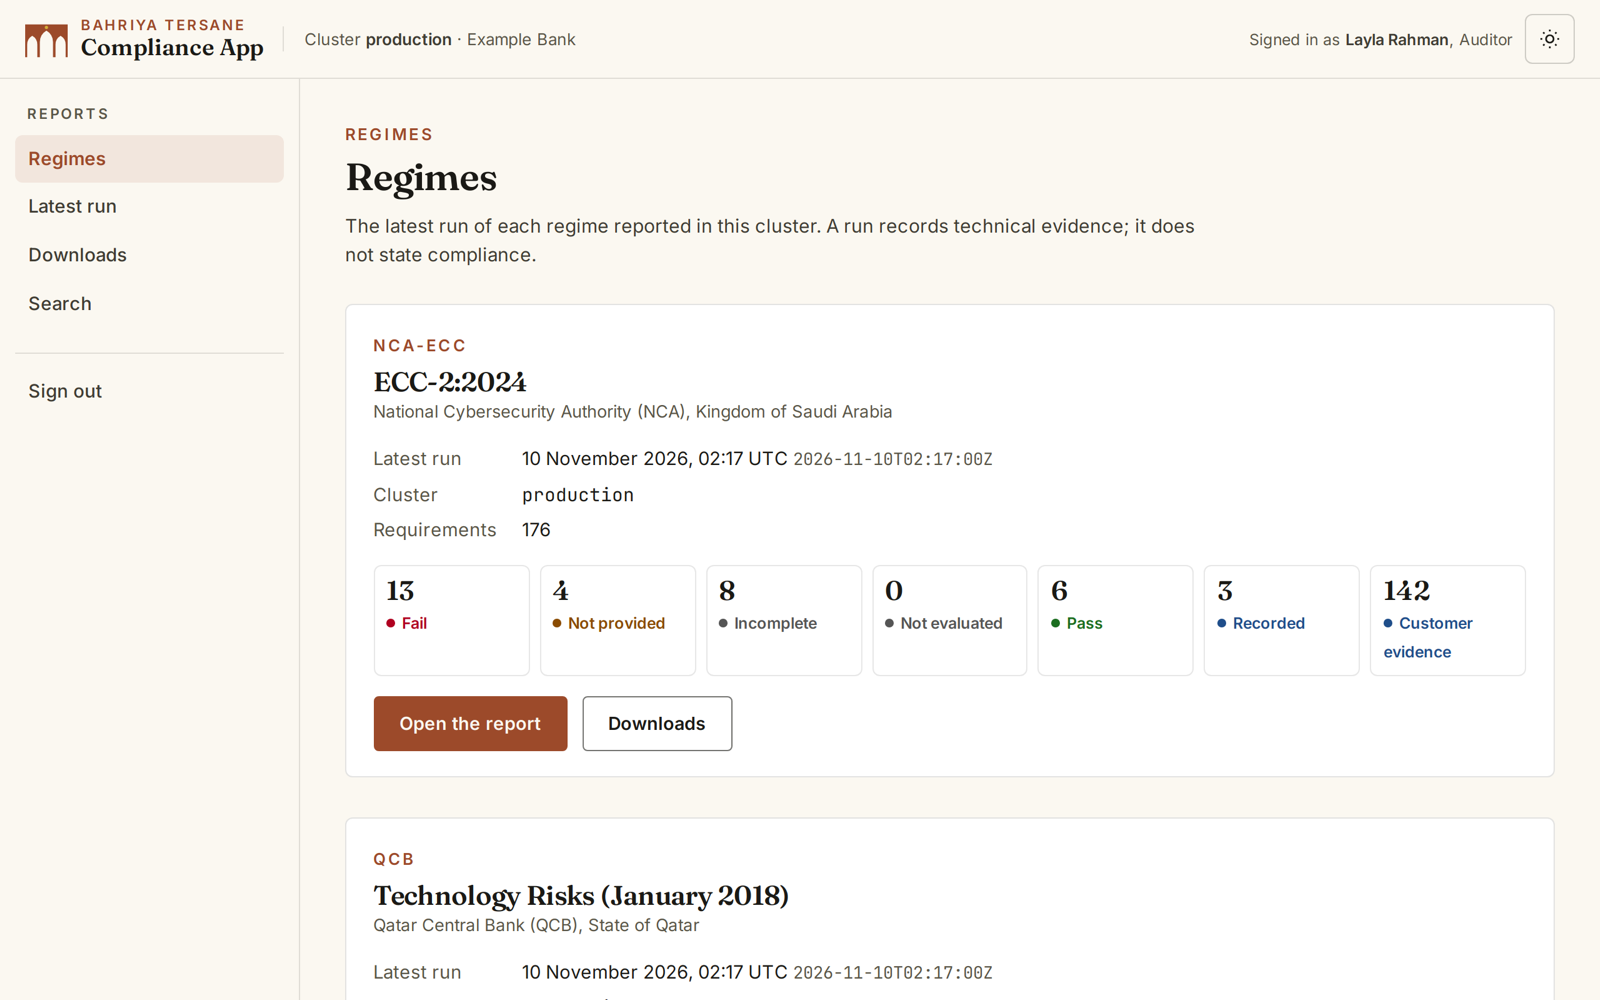
Through your identity provider, or local accounts.
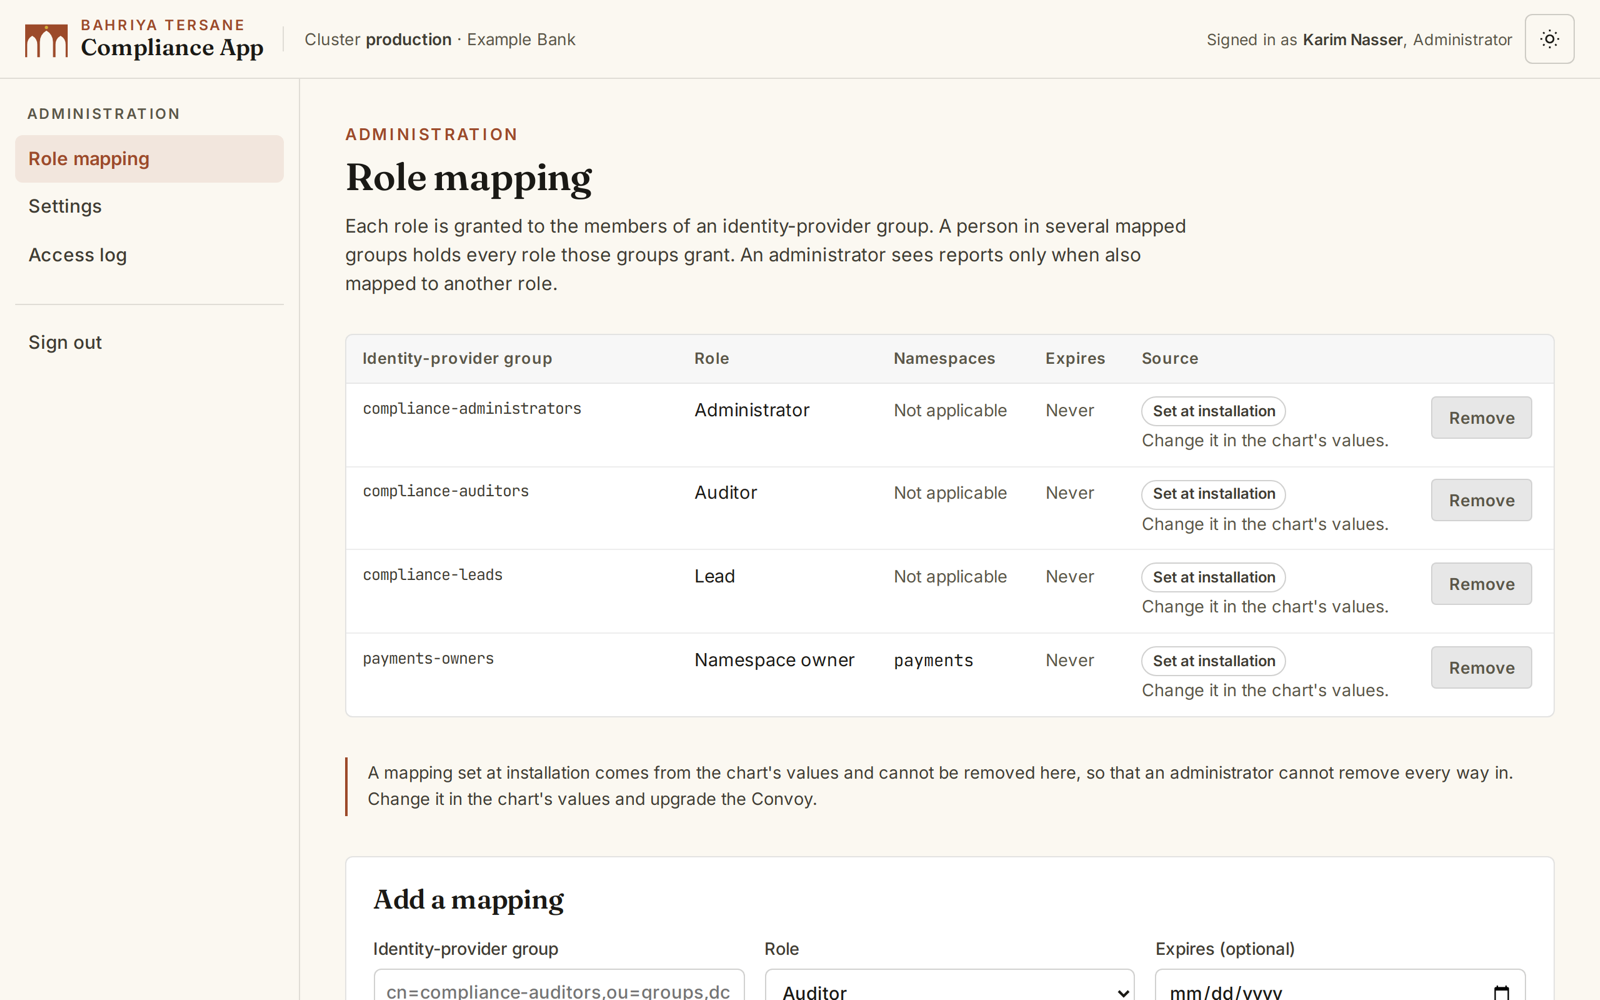
People sign in through your organisation's own identity provider, by OpenID Connect, or, where no provider is connected yet, with local accounts defined in a Kubernetes Secret. Each person's role comes from the groups the identity provider reports for them: a group is mapped to a role when the convoy is installed, and an administrator can add further mappings in the app, each with an optional expiry.
Roles and scope
Each person sees what their role allows.
| Role | What it sees |
|---|---|
| Auditor | Every regime and every run, read-only, with each requirement's checks and failing objects, and the run's files. |
| Compliance lead | What an auditor sees, and each regime's results over time. |
| Namespace owner | The findings in their own namespaces, and what to fix first there; no cluster-wide finding and no other namespace. |
| Administrator | The settings, the role mappings and the access log, and no report unless also given another role. |
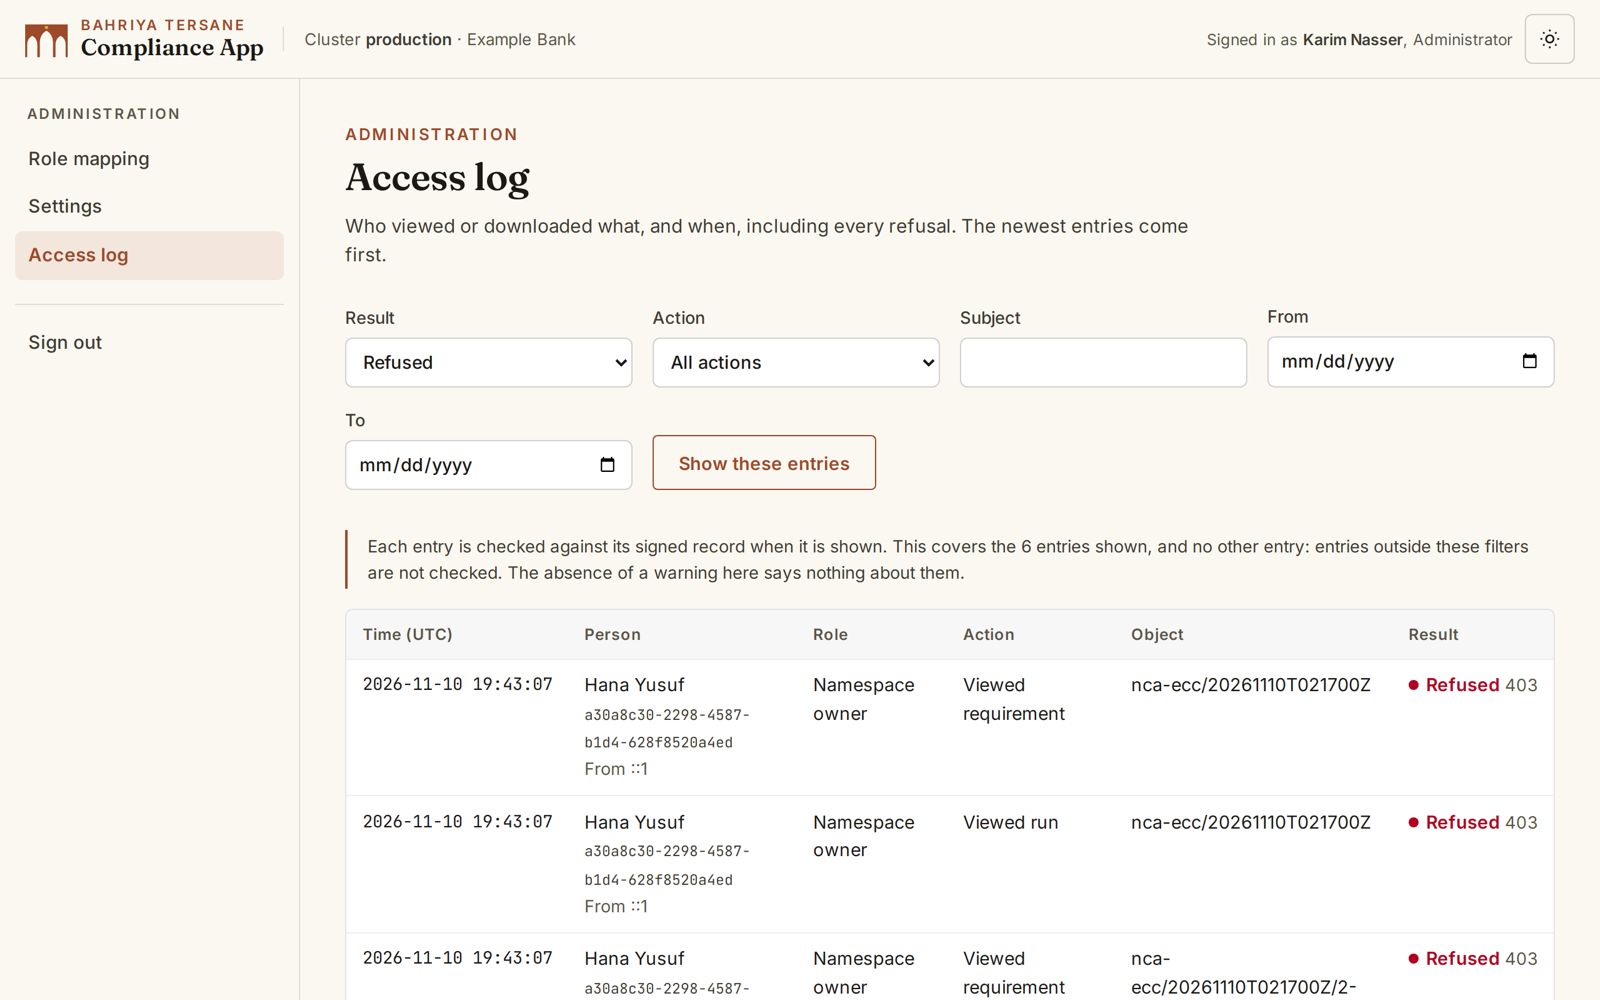
The scope is enforced by the server for every page and every file, not by the screens. A request outside a person's role is refused and recorded in the access log as a refusal. A person in several mapped groups holds every role those groups grant.
For an auditor
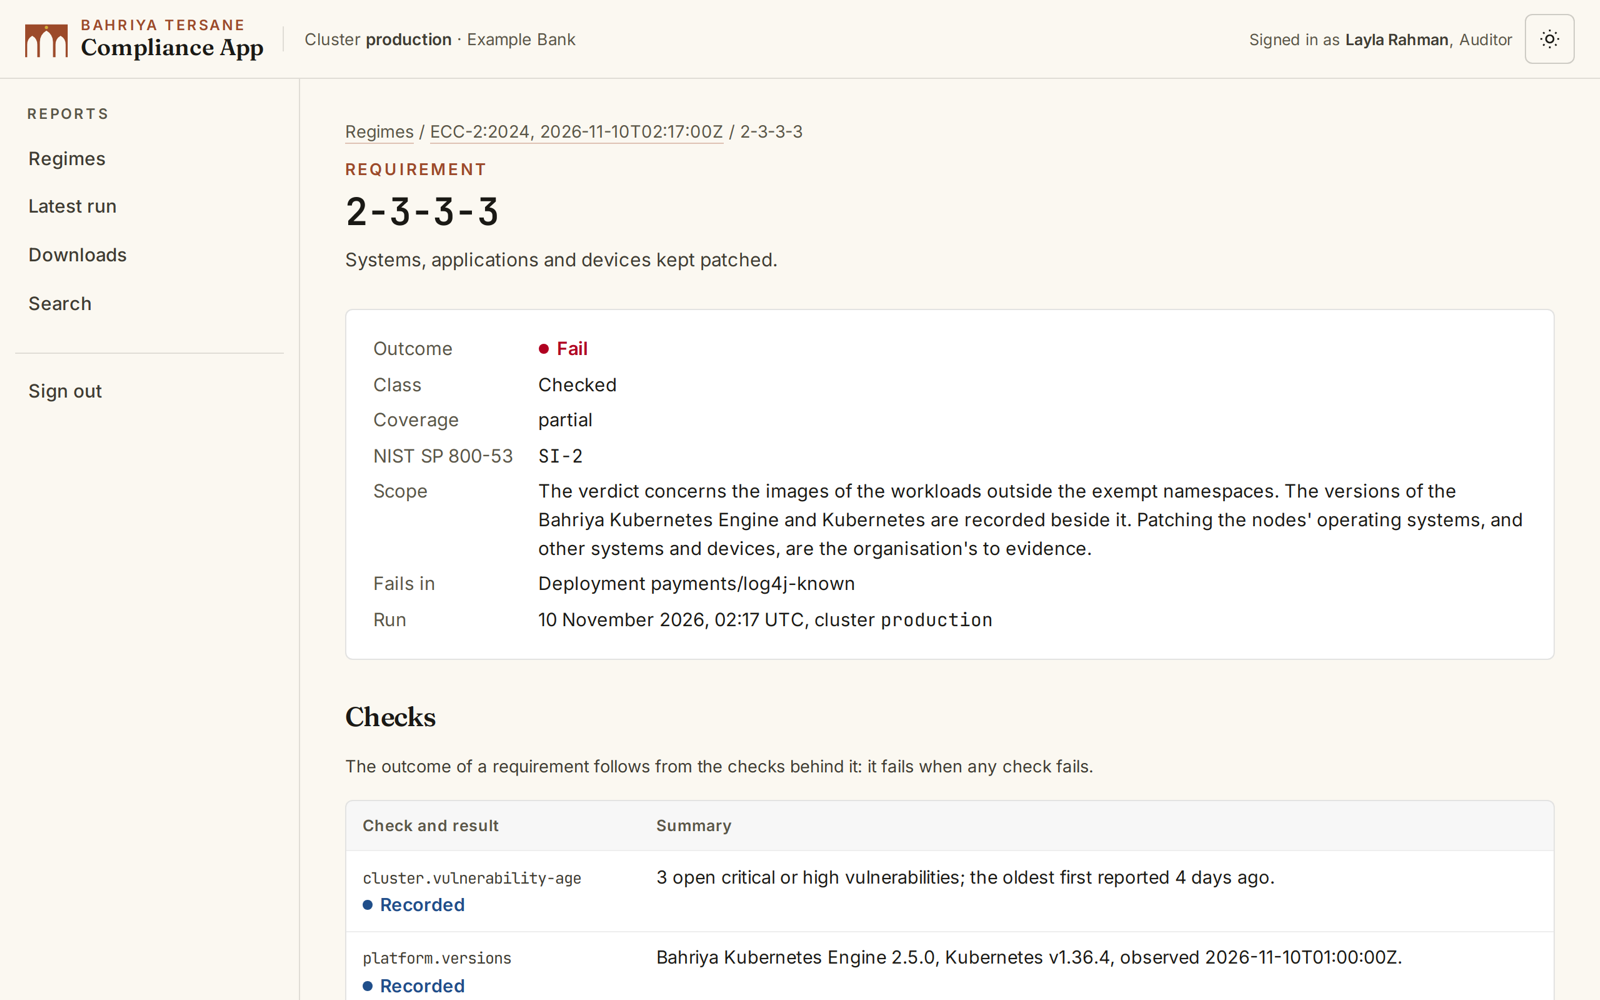
Every requirement, with the evidence behind it.
Each regime is shown requirement by requirement, under the regulator's own identifiers, with exactly one result per requirement. A technical requirement shows the checks behind its verdict and the objects that fail them; an organisational one is listed as the organisation's to evidence, not counted as passed.
For a compliance lead
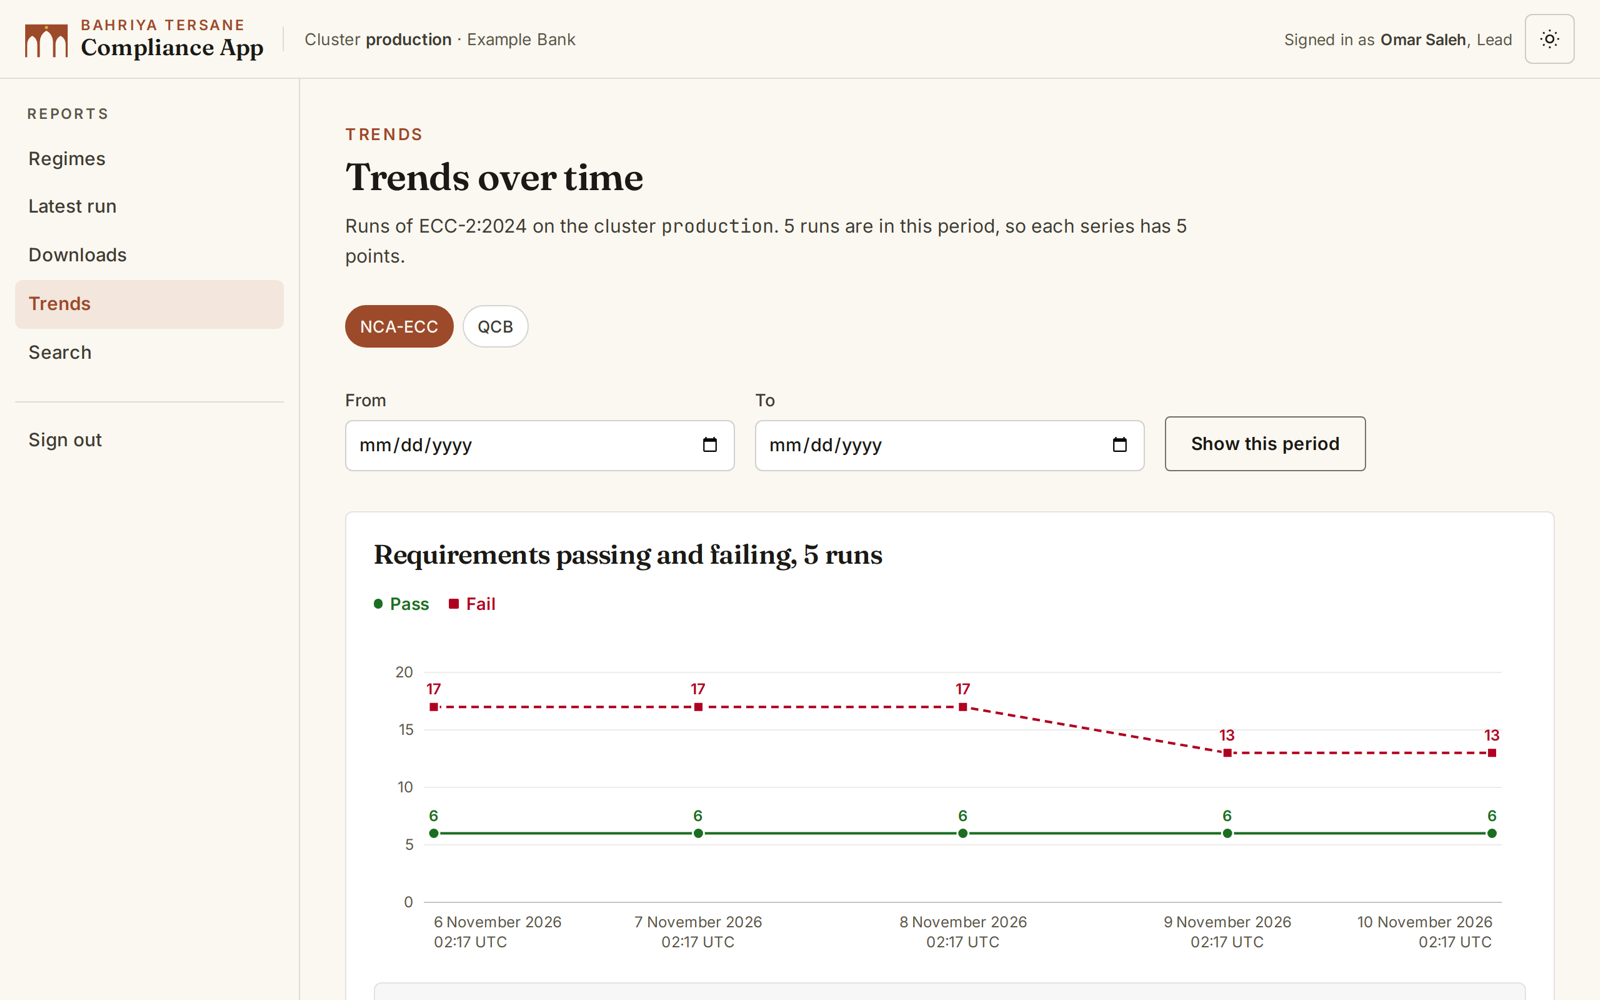
Results over time.
A compliance lead sees each regime's requirements passing and failing, run by run, over any period, so that progress, or a regression, is visible without comparing reports by hand.
For a namespace owner
What to fix first, in your own namespaces.
The owner of an application sees each object in their namespaces that fails a check, most severe first, with the requirements it fails, what is wrong and how to fix it. Fixing an object clears its failure in every requirement listed against it. Cluster-wide findings and other namespaces are not shown to them.
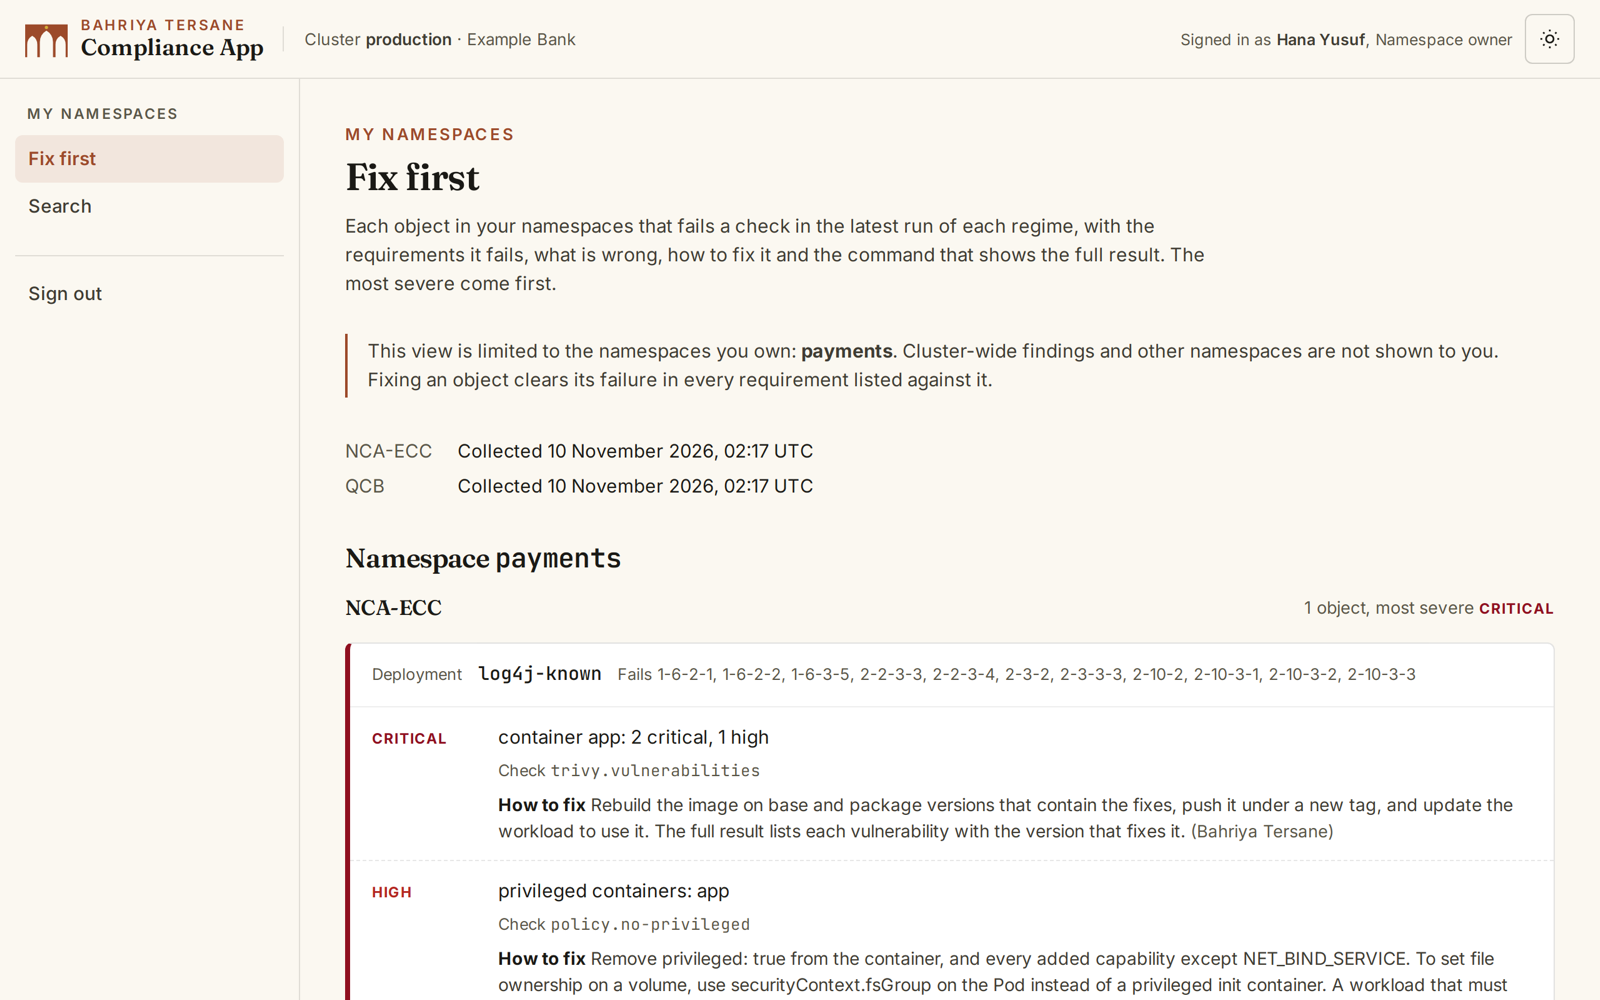
payments sees it: only that namespace, most severe first.Downloads
The run's files, as they were written.
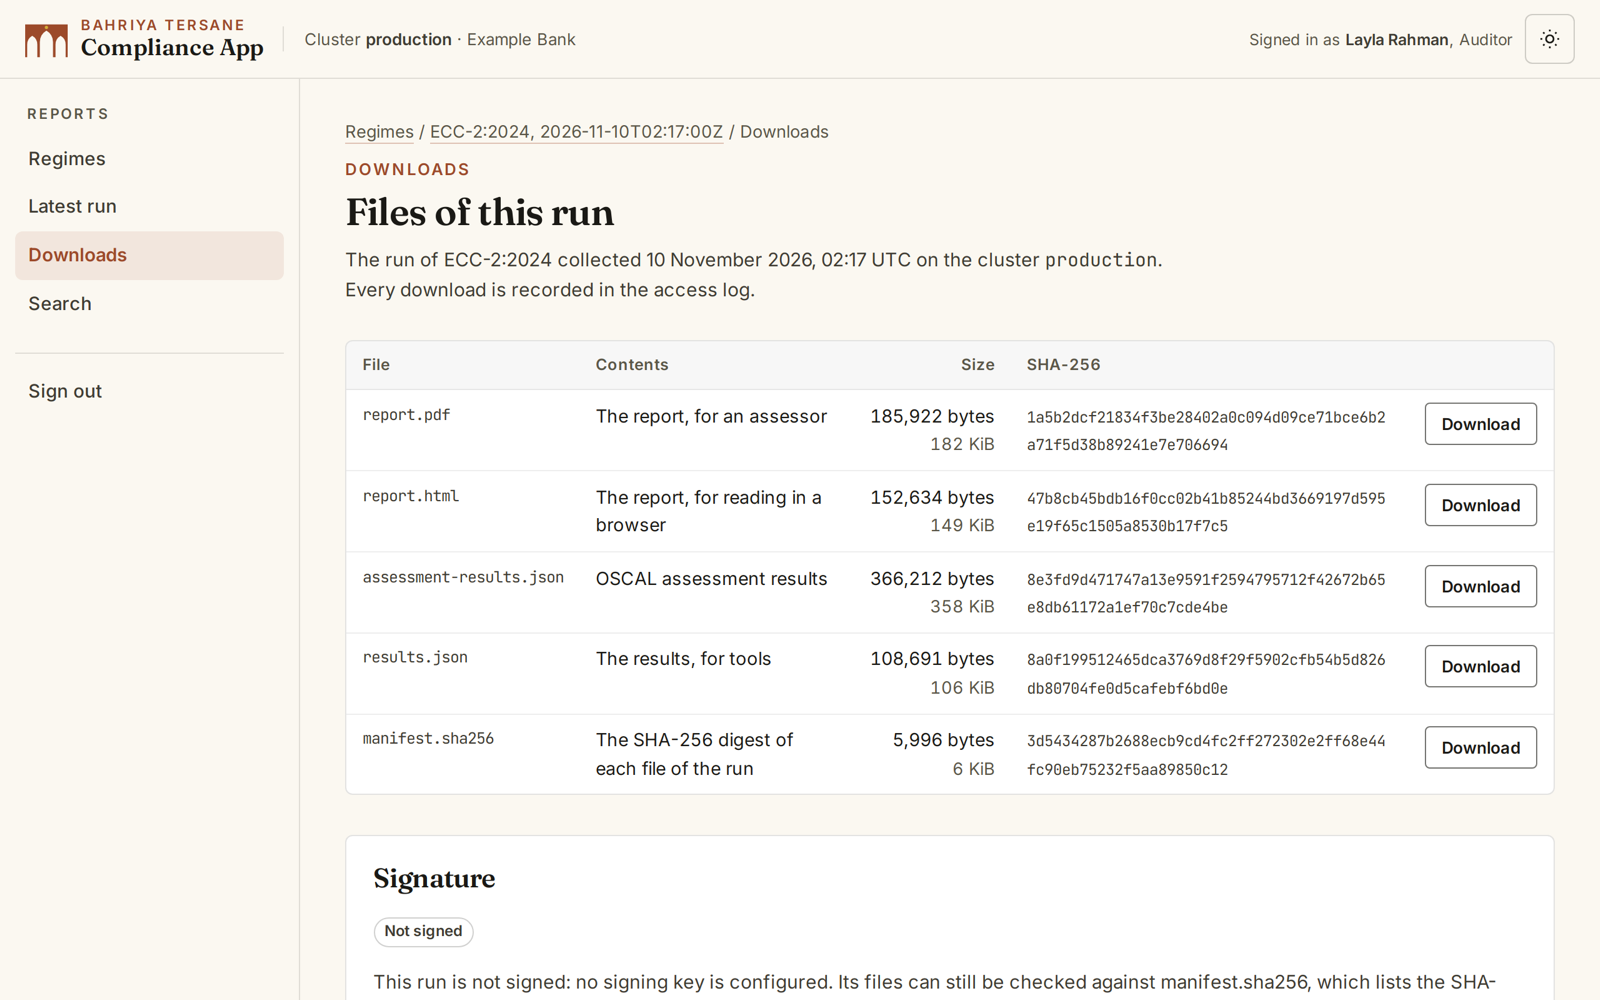
Every file the convoy writes for a run can be downloaded: the report in PDF and HTML, the OSCAL assessment results, the results for tools, and the manifest of SHA-256 digests. Each file is checked against the manifest before it is served, and a file that no longer matches is not served. Every download is recorded in the access log.
For an administrator
Role mapping and the access log.
The mappings set at installation are listed and cannot be changed in the app, so that an administrator cannot remove every way in; further mappings can be added there, each with an optional expiry. The access log records every request to a report, a run or a file, allowed or refused, with the person, the role, the action and the result. Each entry is signed, and an entry changed after it was written is shown as not matching its signed record. A read that cannot be recorded is refused rather than served unrecorded.
Installation
Switched on in the convoy's chart.
The app is installed with the convoy's chart and takes the place of the convoy's web view.
complianceApp.enabled switches it on; the identity provider's issuer, client and
audience, its network addresses and at least one administrator mapping are required, and the chart
refuses to render without them. You publish the app's Service through an Ingress of your own, with
your certificate.
complianceApp:
  enabled: true
  oidc:
    issuer: https://idp.example.com/realms/example
    clientId: compliance
    audience: compliance
    egressCidrs: ["192.0.2.10/32"]
  roles:
    - {group: platform-admins, role: administrator}
    - {group: auditors, role: auditor}
    - {group: team-a, role: namespace-owner, namespaces: [team-a]}
  ingressFrom: [ingress-nginx]
A NetworkPolicy limits what the app may reach to DNS and the identity provider's addresses. The convoy's documentation describes every value.
What it does not do
It reads evidence.
- It does not certify compliance. The organisational requirements of each regime remain your organisation's to evidence, and compliance is determined by your assessor.
- It does not change the evidence. It reads the convoy's volumes read-only, and serves a file only while it matches the run's manifest.
- It does not replace the regime's text. The mapping of each regime's requirements to the cluster's controls is Mamluk's reading of the regime; the authoritative wording remains the regulator's.
Price and availability
The Compliance App is licensed as an add-on to the Compliance and Assurance Convoy at USD 12,000 per organisation, per year, whatever the number of regimes. The convoy is licensed at USD 24,000 per regulatory regime, per organisation, per year, with the Tersane core licence; its own web view and email reports remain included without the app. The app shows the regimes your licence holds. Available today: NCA ECC, QCB and UAE IA; the regimes that follow are listed on the convoy's page.
Discuss the app
To discuss the Compliance App, the regimes your organisation must meet, or the convoy's licensing, contact Mamluk.
Contact Mamluk